Why This Matters Now
Every major platform vendor — Apple, Google, and Microsoft — has shipped passkey support across its operating systems and browsers. Password managers like 1Password and Bitwarden now store and sync passkeys alongside passwords. Banks, SaaS vendors, and government portals are adding "sign in with a passkey" as an option, and in some cases making it the default.
For security teams and people building a career in this field, this is no longer a future-tense conversation. Clients, auditors, and leadership are asking the same question: should we move users off passwords and onto passkeys, and how fast?
This article explains what passkeys actually are under the hood, where they genuinely close security gaps, where they don’t, and how to run a realistic rollout — including for resource-constrained SMBs.
What a Passkey Actually Is: FIDO2 and Passwordless Authentication Basics
A passkey is not a stronger password. It’s a credential based on public-key cryptography — part of the broader shift toward passwordless authentication — built on the FIDO2/WebAuthn standard jointly developed by the FIDO Alliance and the W3C.
When a user creates a passkey for a website or app:
- The device (phone, laptop, or a hardware security key) generates a cryptographic key pair.
- The private key never leaves the device — it’s stored in a secure enclave, TPM, or equivalent hardware-backed store.
- The public key is sent to and stored by the relying party (the website/service).
- At login, the service sends a cryptographic challenge; the device signs it with the private key and returns the signature.
- The server verifies the signature against the stored public key. No secret ever travels over the network, and nothing shared with the server could be stolen and replayed elsewhere.
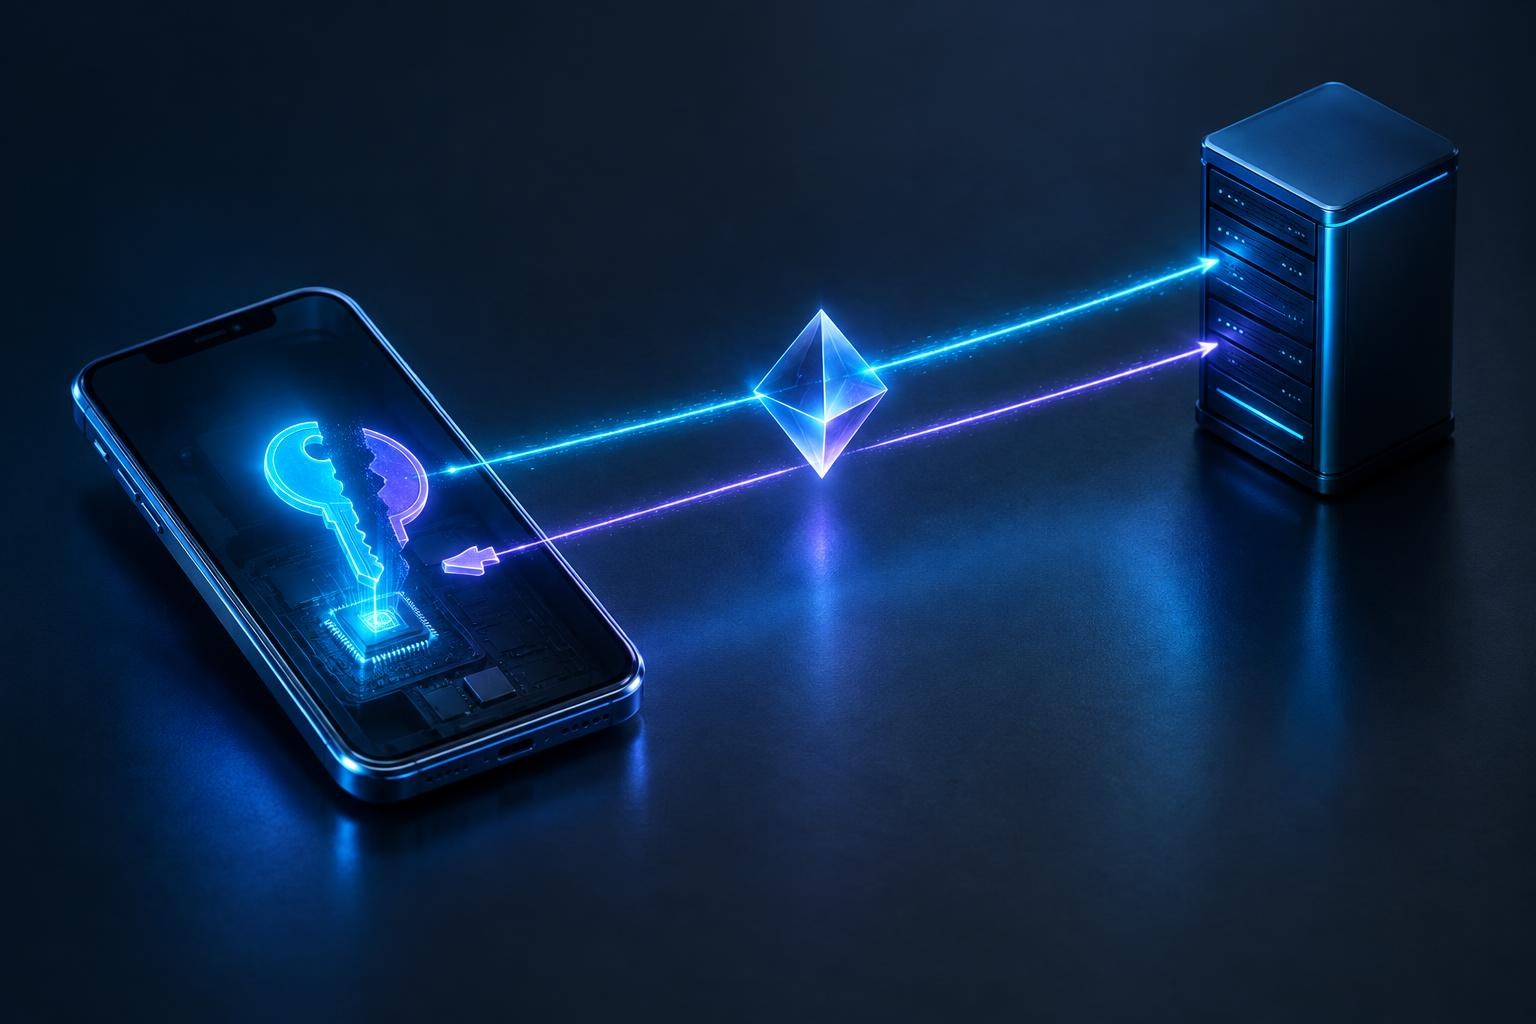
This is the core difference from passwords: there is no secret to phish, no database of hashes to crack, and no credential that works on a second, look-alike domain.
Platform vs. Roaming Authenticators
- Platform authenticators live on the device itself — Face ID/Touch ID on Apple devices, Windows Hello, Android biometrics. The private key is synced via the platform’s cloud keychain (iCloud Keychain, Google Password Manager) so it’s available across a user’s own devices.
- Roaming authenticators are external hardware, such as YubiKeys or other FIDO2 security keys. These are not tied to one ecosystem and are the preferred option for high-assurance use cases (admins, executives, developers with production access).
What Passkeys Fix That Passwords Can’t
They remove credential phishing as a viable attack path. A passkey is cryptographically bound to the exact origin (domain) it was created for. A fake login page at micr0soft-login.com cannot trigger a valid passkey response for microsoft.com — the browser and OS enforce this at the protocol level. This is the single biggest reason organizations are moving toward phishing-resistant authentication.
They eliminate password reuse risk. There’s no password for a user to reuse across your HR portal, their personal email, and a breached e-commerce site. Credential-stuffing attacks that rely on leaked password lists simply don’t apply to passkey-protected accounts.
They remove shared-secret database risk. If an attacker breaches your authentication server, they get public keys — useless for logging in anywhere. Compare this to a stolen password hash database, which can be cracked offline indefinitely.
They reduce support overhead. No "forgot password" resets, no password complexity complaints, no helpdesk tickets for lockouts caused by expired rotation policies.
Google has publicly stated that none of its employees have been successfully phished since it mandated hardware security keys (a FIDO precursor to passkeys) for staff — a frequently cited real-world data point for phishing-resistant authentication at scale.
US federal guidance has also moved decisively in this direction. OMB Memorandum M-22-09 requires federal agencies to implement phishing-resistant MFA, and NIST SP 800-63B explicitly defines phishing-resistant authenticators — syncable and device-bound passkeys qualify at AAL2/AAL3 depending on implementation. This is useful context even outside US federal environments, because it’s increasingly the reference model auditors point to.
Where Passkeys Still Fall Short
Account recovery is the new weak point. If phishing is defeated, attackers pivot to abusing recovery flows — "I lost my phone, let me back in." If your recovery process falls back to email OTP or a security question, you’ve reintroduced a phishable path. Recovery design matters as much as the passkey itself.
Cross-ecosystem UX is still inconsistent. A passkey created in Apple’s keychain doesn’t automatically sync to a Windows laptop. Cross-device sign-in works via Bluetooth proximity and QR codes (hybrid transport), but it’s an extra step users notice, especially early on.
Legacy and on-prem systems often don’t support WebAuthn at all. Many ERPs, VPN clients, and internal line-of-business apps still require username/password or RADIUS. Passkeys can’t be dropped in everywhere — password-based or SAML/OIDC federated access will coexist with passkeys for years in most organizations.
Enterprise management tooling is still maturing. Centrally provisioning, auditing, and revoking passkeys at scale (equivalent to a password policy in Active Directory) depends on your identity provider’s current feature set — this varies significantly between Entra ID, Okta, and Google Workspace, and capabilities are still being added.
Shared or kiosk-mode devices are awkward. Passkeys are tied to a device or a synced account; shared workstations (common in retail, healthcare front desks, warehouses) don’t map cleanly onto a "my device, my biometric" model. Hardware security keys that roam with the employee are the practical workaround.
A Practical Passkey Rollout Plan for SMBs
Step 1: Inventory your authentication surface
List every system your organization uses and mark which ones support WebAuthn/FIDO2 natively today (check your identity provider’s and each SaaS vendor’s documentation). Separate into three buckets: passkey-ready now, passkey-ready via your IdP (federated SSO), and password-only for the foreseeable future.
Step 2: Start with your identity provider, not every app
If you’re on Microsoft Entra ID, Okta, or Google Workspace, enabling passkeys at the IdP level immediately covers every app federated through SSO — this is the highest-leverage first move and typically doesn’t require per-app configuration.
Step 3: Pilot with a high-value, low-friction group
IT admins and developers are good pilot candidates — they understand the UX change, and they’re also your highest-value targets for credential theft. Use hardware security keys for this group where production access is involved, since they’re portable, revocable, and not tied to a personal device backup.
Step 4: Redesign account recovery before go-live
Define a recovery process that doesn’t quietly reintroduce a phishable fallback. Options include a second registered passkey, admin-assisted identity verification with video/ID check, or a backup hardware key stored securely. Document this before wide rollout — it’s the part attackers will target first.
Step 5: Keep passwords as a managed fallback, not a parallel default
Don’t ask most users to choose between a password and a passkey every time — that decision fatigue leads people back to passwords out of habit. Configure passkeys as the default/first option and restrict password login to accounts that genuinely need it.
Step 6: Train users on what’s actually different
The biggest adoption blocker isn’t technical, it’s trust. Users don’t intuitively understand that a passkey isn’t "just Face ID" or that it can’t be phished the way a password can. A short explanation — "this proves it’s really you to the real site, not a copy" — resolves most hesitation.
Common Mistakes and Misconceptions About Passwordless Authentication
"Passkeys are MFA, so we can drop our other MFA requirements." A passkey is a single, strong, phishing-resistant factor. For high-assurance roles (finance approvals, admin access to production), many organizations still layer passkeys with an additional control, such as device compliance checks or conditional access policies — not because the passkey is weak, but because defense-in-depth doesn’t disappear with one strong factor.
"Passkeys mean we can ignore device security." If an attacker gains control of an unlocked, logged-in device, the synced passkey is usable on that device. Passkeys shift risk from "credential theft over the network" to "endpoint compromise" — endpoint hardening and screen-lock policies remain essential.
"This is only relevant to consumer apps." B2B SaaS, banking portals, and government services across the GCC are adding passkey support at a growing rate. Treating this as a consumer-only trend means your organization will be behind when clients or regulators start asking about phishing-resistant authentication specifically.
"Rollout has to be all-or-nothing." It doesn’t. A phased approach — IdP first, high-value users second, broad rollout third — delivers most of the risk reduction early without a disruptive big-bang cutover.
"Passkeys solve social engineering entirely." They close the technical phishing vector (fake login pages), but they don’t stop a user from being talked into installing malware, approving a fraudulent push notification on an unrelated system, or authorizing a fraudulent wire transfer. Passkeys protect authentication, not every form of social engineering.
FAQ
Are passkeys really unphishable?
Yes, for the specific attack of a fake login page capturing credentials — the browser/OS cryptographically ties the passkey to the legitimate origin, so a lookalike domain cannot obtain a valid signature. They don’t protect against malware on an already-compromised, unlocked device, or against social engineering that doesn’t involve a fake login page.
What happens if someone loses their phone?
If the passkey was synced (iCloud Keychain, Google Password Manager), it’s recoverable by signing into the same account on a new device. If it was device-bound with no sync (e.g., a hardware security key with no backup registered), the user needs a pre-defined recovery path — which is why Step 4 above matters before rollout, not after.
Can passkeys be shared among a team, like a shared admin login?
Not in the way shared passwords often are today, and that’s largely intentional — shared credentials are a known audit and accountability problem. The better pattern is individual passkeys per person with role-based access control, rather than trying to replicate password-sharing habits.
Do passkeys replace the need for a password manager?
For accounts that support passkeys, largely yes — the OS/browser keychain or the password manager itself (1Password, Bitwarden) now generates and stores passkeys the same way it stored passwords. For accounts that don’t yet support passkeys, you’ll still need the password manager for standard password storage and generation.
Is this realistic for a small business with limited IT budget?
Yes, in phases. Start with your identity provider and major SaaS tools (Microsoft 365, Google Workspace), which already include passkey support at no extra cost. Hardware security keys for a handful of privileged accounts (owner, finance, IT) cost roughly $25–$60 per key — a small investment against the cost of a single business email compromise.
Free Resources
- FIDO Alliance – Passkeys Overview — Vendor-neutral explanation of the standard, adoption tracker, and implementer resources.
- W3C WebAuthn Specification — The formal technical standard underlying passkeys, for teams implementing WebAuthn directly.
- NIST SP 800-63B – Digital Identity Guidelines: Authentication and Lifecycle Management — Defines authenticator assurance levels and phishing-resistant authentication criteria.
- CISA – Implementing Phishing-Resistant MFA — Practical fact sheet on phishing-resistant authentication methods, including passkeys/FIDO2.
- passkeys.dev — Vendor-backed developer resource with implementation guides, platform support tables, and UX recommendations.
Conclusion
Passkeys solve a specific, high-impact problem: they make the most common form of credential theft — phishing a password off a fake login page — technically impossible against the systems that support them. That alone justifies moving your identity provider and high-value accounts onto passkeys in 2025.
They are not a universal password replacement yet. Legacy systems, enterprise management tooling, and account recovery design all need deliberate planning, and passwords will coexist with passkeys in most environments for years.
Next step: inventory which of your core systems (starting with your SSO/identity provider) already support WebAuthn, and run a passkey pilot with your IT/admin group before year-end. That single move removes your highest-risk accounts from the phishing attack surface with minimal cost or disruption.