Why Firewall Rules Are a PCI DSS Compliance Problem, Not Just a Technical One
Small and mid-sized businesses that take card payments, or that handle cardholder data on behalf of a client, are in scope for PCI DSS whether they have a dedicated security team or not. Many SMBs assume a consumer-grade router with "firewall enabled" is good enough. It isn’t, and QSAs (Qualified Security Assessors) know it.
PCI DSS Requirement 1.2.1 (PCI DSS v3.2.1, carried forward conceptually into the Requirement 1 network security control rules in PCI DSS v4.0) states that organizations must "restrict inbound and outbound traffic to that which is necessary for the cardholder data environment, and specifically deny all other traffic." In plain terms: your firewall must default to blocking everything, then explicitly allow only the specific protocols, ports and hosts your business actually needs. A flat "allow all" rule, or a rule set that was never cleaned up after a vendor integration project, is a textbook finding in a PCI assessment — and a textbook way for an attacker to move laterally once they get a foothold.
The real-world consequence is not abstract. Breach investigations into SMB point-of-sale compromises repeatedly show the same pattern: a firewall with permissive outbound rules let malware on a POS terminal reach a command-and-control server unimpeded, or a permissive inbound rule exposed a management interface to the internet. Commercial next-generation firewalls that do this well can cost thousands of dollars a year in licensing — a real barrier for a 15-person retailer or a regional service provider.
pfSense Community Edition (CE) closes that gap. It is a free, open-source firewall and router platform built on FreeBSD’s pf packet filter, and it gives an SMB the same rule granularity, logging and segmentation capability that a QSA expects to see from an enterprise appliance — at the cost of a spare PC or a small VM.
This article walks through configuring pfSense to satisfy the PCI DSS firewall requirement in Requirement 1.2.1 — installing pfSense, building a default-deny rule base, verifying it, and keeping evidence a QSA can review.
Prerequisites: What You Need Before Configuring pfSense for PCI DSS
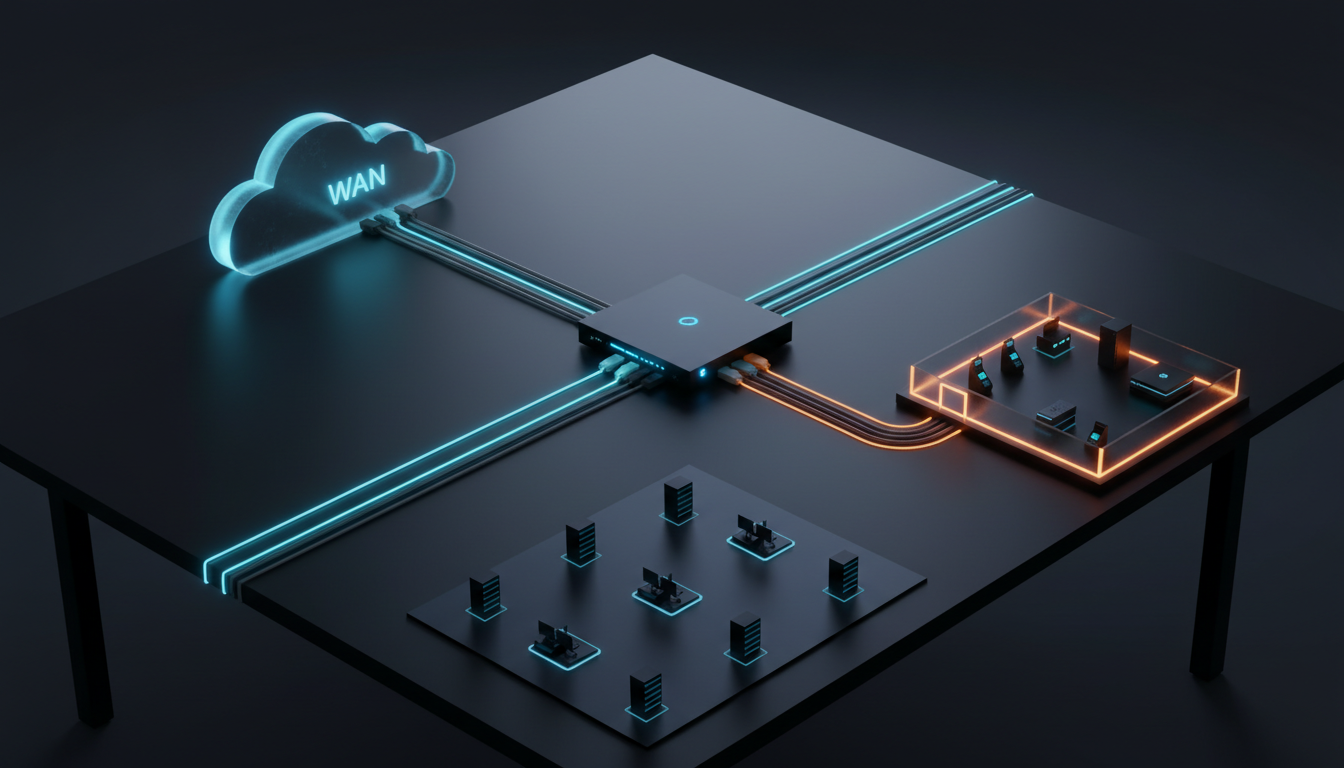
- A dedicated device for pfSense: a spare PC/mini-PC with at least two NICs, or a VM (ESXi, Proxmox, Hyper-V) with two virtual NICs — one for WAN, one for LAN. A third NIC is useful if you plan to segment a cardholder data environment (CDE) into its own zone, which Requirement 1.3 also expects.
- The pfSense CE ISO, downloaded from the official Netgate site (netgate.com/pfsense), plus its published SHA256 checksum.
- Console or IPMI/iDRAC access to the box for initial setup (no GUI exists until interfaces are assigned).
- A documented list of what traffic your business actually needs: which services, which ports, which directions (inbound/outbound), and which hosts. This list is the input to your rule base — pfSense can’t write it for you, and a QSA will ask to see it as your "configuration standard" per Requirement 1.1.
- Basic familiarity with TCP/IP, subnetting, and your current network diagram.
- An admin workstation on the same LAN segment for initial WebGUI access.
Step-by-Step: Building a pfSense Default-Deny Rule Base for PCI DSS Requirement 1.2.1
1. Verify the installer before you trust it
sha256sum pfSense-CE-2.7.2-RELEASE-amd64.isoCompare the output against the checksum published on the official pfSense download page. This confirms the ISO wasn’t corrupted or tampered with in transit — a basic integrity control you want in place before you build anything that will sit at your network edge.
2. Install pfSense and assign interfaces
Boot from the verified ISO, accept the default FreeBSD/ZFS or UFS install options, and let the installer run. On first boot, the console menu will prompt you to assign WAN and LAN interfaces.
Enter the WAN interface name or 'a' for auto-detection: em0
Enter the LAN interface name or 'a' for auto-detection: em1
This tells pfSense which physical NIC faces the internet (WAN) and which faces your internal network (LAN). Verify it worked by checking link state from the console shell:
ifconfig em0 em1Both interfaces should show status: active.
3. Lock down initial WebGUI access
From the admin workstation, browse to https://192.168.1.1 (pfSense’s default LAN IP) and log in with the default credentials (admin / pfsense). Immediately change the password under System > User Manager, and disable WAN access to the WebGUI if it isn’t already (it is blocked by default — confirm it stays that way). This protects the one interface that, if exposed, would let an attacker rewrite your rule base entirely.
4. Define aliases for your cardholder data environment
Under Firewall > Aliases, create a named alias for the systems that actually touch card data — for example, your POS terminals and payment gateway.
Alias name: CDE_HOSTS
Type: Network(s)
Networks: 10.10.20.0/24
Description: Segmented cardholder data environment per PCI DSS Req 1.3
Aliases let you write readable, maintainable rules ("allow CDE_HOSTS to PAYMENT_GATEWAY on 443") instead of raw IP lists, which is exactly the kind of documented, auditable configuration a QSA wants to see mapped to Requirement 1.1.5 (review of rule sets).
5. Remove the implicit trust and start from deny
pfSense’s LAN interface ships with a default "allow LAN to any" rule. This is the opposite of what Requirement 1.2.1 demands. Go to Firewall > Rules > LAN and delete (or disable) that default allow-all rule.
Action: Pass | Interface: LAN | Protocol: * | Source: LAN net | Destination: * -> DELETE THIS RULEVerify it’s gone by checking the active rule set from the shell:
pfctl -sr | grep "lan"You should no longer see a rule permitting LAN-to-any traffic unconditionally.
6. Build explicit allow rules, narrowest first
For each item on your documented "traffic that is actually necessary" list, add one specific rule. Order matters — pfSense evaluates top to bottom and uses the first match.
Rule 1:
  Action: Pass
  Interface: LAN
  Protocol: TCP
  Source: CDE_HOSTS
  Destination: PAYMENT_GATEWAY
  Destination port: 443
  Description: PCI Req 1.2.1 - CDE to payment processor, HTTPS only

Rule 2:
  Action: Pass
  Interface: LAN
  Protocol: UDP
  Source: LAN net
  Destination: LAN address
  Destination port: 53
  Description: Internal DNS resolution only
Each rule should state a business reason in the description field — this becomes your audit trail.
7. Add the explicit "deny all else" rule and log it
At the bottom of the LAN rule set, add a catch-all deny rule with logging enabled.
Rule (last):
  Action: Block
  Interface: LAN
  Protocol: *
  Source: *
  Destination: *
  Log: Enabled
  Description: PCI Req 1.2.1 - deny all other traffic, default implicit deny made explicit
Technically, pf already denies unmatched traffic by default, but adding an explicit, logged "deny all" rule gives you visible evidence for the assessor and a log entry for every traffic attempt that didn’t match an approved rule.
8. Verify the rule base is actually enforcing what you think it is
pfctl -srRead through the output top to bottom and confirm the order matches the GUI: specific allows first, explicit block-and-log last. Then generate test traffic from a host that should be blocked (e.g., an unapproved outbound port) and confirm it’s dropped:
nc -vz -w 3 8.8.8.8 23Check Status > System Logs > Firewall in the WebGUI — you should see the blocked attempt logged with the rule description from Step 7.
9. Enable and schedule configuration backups
Under Diagnostics > Backup & Restore, or via the free AutoConfigBackup package (cloud-hosted by Netgate) or a local scheduled export, keep dated copies of config.xml. This is both an operational safeguard and compliance evidence that your rule base changes are tracked over time (relevant to Requirement 1.1.1’s change-control expectations).
scp admin@pfsense.local:/cf/conf/config.xml ./backups/pfsense-config-$(date +%F).xmlVerify the backup by opening the XML file and confirming it contains your <rule> entries from Steps 5–7. If you also manage Linux servers via SSH elsewhere in your environment, the same least-privilege, audit-ready mindset applies — see our guide to hardening SSH on Linux servers for CIS-aligned settings you can apply there too.
10. Document the rule base review
PCI DSS expects firewall rule sets to be reviewed at least every six months (Requirement 1.1.7 in v3.2.1; carried into the
[Output was cut off at the length limit.]