Blog
Security Fatigue: Why Your Team Stops Caring About Warnings
Security fatigue causes employees to ignore warnings and skip MFA. Learn why it happens and 3 practical steps GRC teams can take this week.
Step-by-Step: Deploying Suricata IDS/IPS on a Linux Server for Real-Time Threat Detection
Set up Suricata IDS/IPS on Ubuntu Linux step by step: install, configure detection, update rules, verify alerts, and enable inline blocking.
Colonial Pipeline Ransomware Attack: How a Single Compromised Password Shut Down Critical Infrastructure
How one leaked VPN password caused the Colonial Pipeline ransomware shutdown — root cause, timeline, and the controls that would have stopped it.
Lock Down SMB Network Access for Free: How pfSense Helps You Meet PCI DSS Requirement 1.2.1
See how pfSense PCI DSS compliance works: build a free, documented firewall ruleset that satisfies PCI DSS v4.0 Requirement 1.2.1 for SMBs.
Cybersecurity Resume for Beginners: How to Translate IT or Military Experience into Security Language
Turn IT or military experience into a cybersecurity resume for beginners, with hiring-manager-ready bullets, keywords, and ATS tips.
Passkeys vs Passwords: A Security Guide for 2025
Passkeys vs passwords security: how FIDO2 works, what it fixes, where it falls short, and a rollout plan for SMBs.
Step-by-Step: Hardening a Linux Server with CIS Benchmarks and Lynis (Free, Open-Source)
Harden Linux with CIS Benchmark controls and Lynis: install, run a free audit, fix the top 10 findings, and track your hardening score.
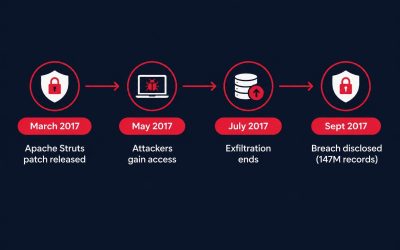
Equifax 2017 Breach: Root Cause and Lessons Learned from an Unpatched Apache Struts Flaw
Equifax breach root cause: an unpatched Apache Struts flaw (CVE-2017-5638) exposed 147M records. Lessons learned and controls that would have stopped it.
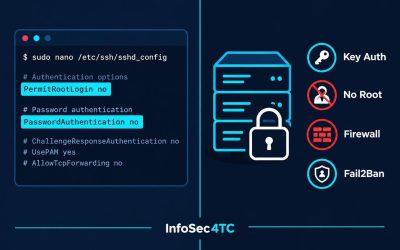
Hardening SSH on Linux Servers: A Step-by-Step CIS Benchmark Guide
Harden SSH on Linux servers with this CIS Benchmark guide: key-based auth, ciphers, logging, Fail2Ban setup, and a verification checklist.